
Win32/Virlock. Y

What Is Win32/Virlock. Y Infection? in This Short Article You Will Certainly Locate About the Meaning of Win32/Virlock. Y and Also Its Adverse Influence on...
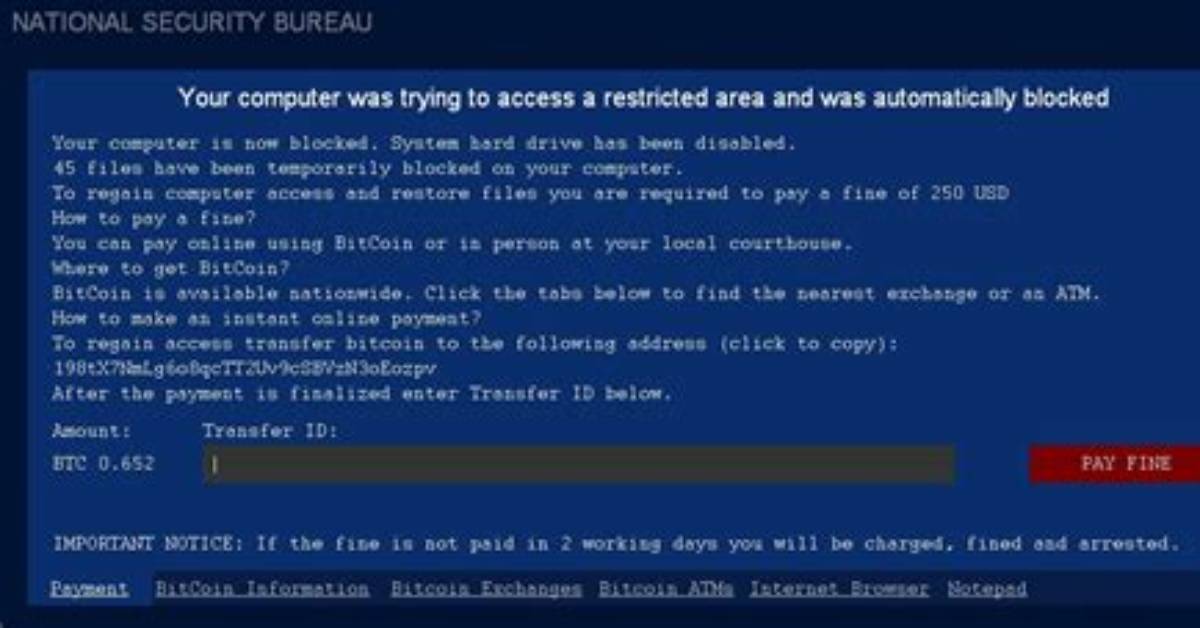
What is Win32/Virlock.Y infection?
In this short article you will certainly locate about the meaning of Win32/Virlock.Y and also its adverse influence on your computer system. Such ransomware are a type of malware that is elaborated by online fraudulences to require paying the ransom money by a sufferer.
In the majority of the situations, Win32/Virlock.Y virus will certainly advise its sufferers to launch funds move for the purpose of neutralizing the amendments that the Trojan infection has actually presented to the victim’s gadget.
Win32/Virlock.Y Summary
These alterations can be as complies with:
- Executable code extraction;
- Creates RWX memory;
- Expresses interest in specific running processes;
- A process created a hidden window;
- Drops a binary and executes it;
- The binary likely contains encrypted or compressed data.;
- The executable is compressed using UPX;
- Uses Windows utilities for basic functionality;
- A process attempted to delay the analysis task by a long amount of time.;
- Attempts to repeatedly call a single API many times in order to delay analysis time;
- Installs itself for autorun at Windows startup;
- Creates a hidden or system file;
- Attempts to disable UAC;
- Attempts to modify Explorer settings to prevent file extensions from being displayed;
- Attempts to modify Explorer settings to prevent hidden files from being displayed;
- Uses suspicious command line tools or Windows utilities;
- Ciphering the files situated on the victim’s hard disk drive — so the victim can no longer make use of the information;
- Preventing regular access to the target’s workstation;
Related domains:
| z.whorecord.xyz | Ransom.PolyRansom.F3 |
| a.tomx.xyz | Ransom.PolyRansom.F3 |
Win32/Virlock.Y
The most typical networks through which Win32/Virlock.Y are infused are:
- By ways of phishing emails;
- As a repercussion of user ending up on a source that hosts a malicious software application;
As soon as the Trojan is efficiently infused, it will either cipher the data on the victim’s computer or protect against the tool from working in a proper fashion – while also placing a ransom note that states the requirement for the targets to effect the repayment for the purpose of decrypting the documents or restoring the data system back to the preliminary condition. In most instances, the ransom note will come up when the client reboots the COMPUTER after the system has already been damaged.
Win32/Virlock.Y circulation networks.
In various corners of the globe, Win32/Virlock.Y expands by jumps and bounds. However, the ransom money notes as well as tricks of extorting the ransom amount might vary relying on particular local (local) settings. The ransom money notes and also tricks of obtaining the ransom money amount may vary depending on particular neighborhood (local) setups.
As an example:
Faulty alerts concerning unlicensed software program.
In certain locations, the Trojans commonly wrongfully report having actually found some unlicensed applications enabled on the target’s gadget. The sharp then requires the user to pay the ransom.
Faulty statements concerning illegal web content.
In countries where software program piracy is less popular, this approach is not as reliable for the cyber scams. Conversely, the Win32/Virlock.Y popup alert might falsely claim to be deriving from a police organization as well as will report having situated child pornography or various other prohibited data on the tool.
Win32/Virlock.Y popup alert may falsely claim to be deriving from a regulation enforcement institution and also will certainly report having located youngster pornography or various other unlawful information on the tool. The alert will likewise have a demand for the individual to pay the ransom.
Technical details
File Info:
crc32: 7FB780F7md5: 5ec48adf56a97a8ef9c8954b0536b0ecname: 5EC48ADF56A97A8EF9C8954B0536B0EC.mlwsha1: 34094ac9cb2bd311fb2b97f4e1bf402c64d9eadesha256: 19578571e88a58b47247b2b0544d6eaac2edd61bbb182fa520a2d6d4e11f598esha512: 6d9182b122beb359094d57189c1bb28a152e44c2bdbbc62d3012de2ce55f5e8d36685875d64dfb066ae52474d1217c58645efd442a7585685ab9bdc8507e8c28ssdeep: 24576:vo8UjQlDS4cYLvNXtRiTy/gL0PtT4m8mTcLDzUnXFkghkhy7apuRKJtk4OT9a:vo8DbFXtRiW/gIPZf8mTM3U65hdpbPztype: PE32 executable (GUI) Intel 80386, for MS Windows, UPX compressedVersion Info:
0: [No Data]
Win32/Virlock.Y also known as:
| GridinSoft | Trojan.Ransom.Gen |
| Bkav | W32.AIDetect.malware1 |
| K7AntiVirus | Trojan ( 004c61081 ) |
| Lionic | Hacktool.Win32.Black.lAAL |
| Elastic | malicious (high confidence) |
| DrWeb | Win32.VirLock.16 |
| Cynet | Malicious () |
| CAT-QuickHeal | Ransom.PolyRansom.F3 |
| ALYac | Gen:Trojan.Heur.inGfrXe4hGni |
| Cylance | Unsafe |
| Zillya | Virus.Virlock.Win32.5 |
| K7GW | Trojan ( 004c61081 ) |
| Cybereason | malicious.f56a97 |
| Symantec | W32.Virlock!inf7 |
| ESET-NOD32 | a variant of Win32/Virlock.Y |
| APEX | Malicious |
| Avast | Win32:Cryptor |
| ClamAV | Win.Virus.Virlock-6840595-0 |
| BitDefender | Gen:Trojan.Heur.inGfrXe4hGni |
| NANO-Antivirus | Virus.Win32.Virlock.dsdros |
| MicroWorld-eScan | Gen:Trojan.Heur.inGfrXe4hGni |
| Tencent | Virus.Win32.VirLocker.j |
| Ad-Aware | Gen:Trojan.Heur.inGfrXe4hGni |
| Sophos | W32/VirRnsm-F |
| Comodo | Backdoor.Win32.Delf.~DP@1mio9l |
| BitDefenderTheta | AI:Packer.B9CF7E421C |
| VIPRE | Virus.Win32.Nabucur.c (v) |
| McAfee-GW-Edition | BehavesLike.Win32.Generic.tc |
| FireEye | Generic.mg.5ec48adf56a97a8e |
| Emsisoft | Gen:Trojan.Heur.inGfrXe4hGni (B) |
| SentinelOne | Static AI – Malicious PE |
| Jiangmin | Trojan.Generic.asutw |
| Avira | TR/ATRAPS.Gen |
| eGambit | Unsafe.AI_Score_100% |
| Antiy-AVL | Trojan/Generic.ASVirus.2BF |
| Microsoft | Trojan:Win32/Wacatac.B!ml |
| GData | Gen:Trojan.Heur.inGfrXe4hGni |
| AhnLab-V3 | Trojan/Win32.PolyRansom.C2334604 |
| McAfee | Artemis!5EC48ADF56A9 |
| MAX | malware (ai score=86) |
| VBA32 | BScope.TrojanRansom.PolyRansom |
| Malwarebytes | PolyRansom.Virus.FileInfector.DDS |
| Rising | Trojan.Win32.Virlock.a (CLASSIC) |
| Yandex | Trojan.GenAsa!QL9iGpbHnpo |
| Ikarus | Virus.Win32.Virlock |
| MaxSecure | Trojan.Malware.300983.susgen |
| Fortinet | W32/Virlock.J |
| AVG | Win32:Cryptor |
| Paloalto | generic.ml |
Maya is a hardware enthusiast who tests and reviews smart home devices, smartphones, wearables, and audio gear. She focuses on practical consumer value and build quality.
