
Wireshark - Sack_Perm=1

We Are Capturing a File Transfer from Machine 1 to Machine 2 via Wireshark. While I Am Unable to Capture Any/Few Retransmission Errors, Other Guy Is Able to...
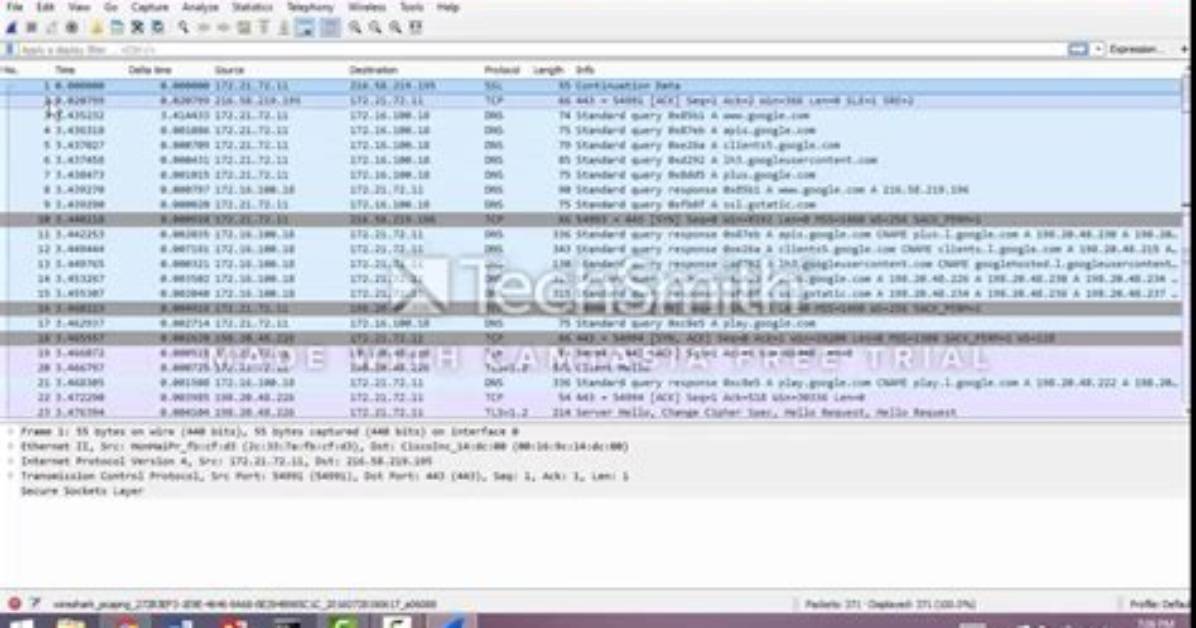
We are capturing a file transfer from machine 1 to machine 2 via Wireshark. While I am unable to capture any/few retransmission errors, other guy is able to capture around 10 to 15 retransmission errors and underrun errors.
On analysing the wire-shark capture, I find that the major difference is that SACK_PERM flag is not set in my capture, whereas SACK_PERM=1 in other capture.
Below is
8535 7.272671 172.23.165.254 10.108.32.29 TCP 62 [TCP Retransmission] 29537 → 389 [SYN] Seq=0 Win=8192 Len=0 MSS=1460 SACK_PERM=1
Can anyone explain the effects of SACK_PERM flag in a network transmission?
Thanks in advance.
1 Answer
That's the "Sack-Permitted" option from RFC 2018, "TCP Selective Acknowledgment Options". It says that the two machines can use "selective acknowledgment", meaning that, instead of just saying "I got all bytes up to this sequence number", they can say "I got all the bytes in this range and all the bytes in this other range", with the implication being that bytes in ranges not listed were not received, so that they can say that they got bytes before and after some ranges, but not the bytes in the middle of the range.
Marcus Vance is a cybersecurity auditor and technology writer dedicated to educating the public about online safety, data privacy regulations, enterprise security, and emerging cyber threats.
