
Your Question: What Is Syslog Service Linux?

Contents Syslog Is the General Standard for Logging System and Program Messages in the Linux Environment. This Service Constitutes the System Log Daemon, Where...
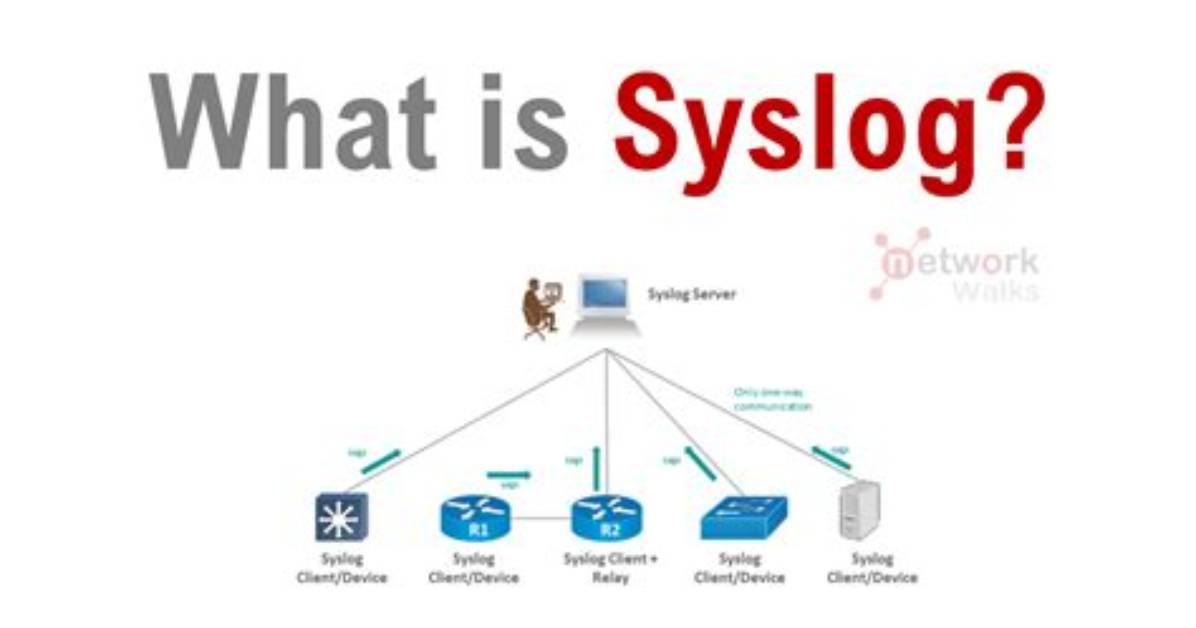
Syslog is the general standard for logging system and program messages in the Linux environment. This service constitutes the system log daemon, where any program can do its logging (debug, security, normal operation) through in addition the Linux kernel messages.
What is syslog in Linux?
Syslog, is a standardized way (or Protocol) of producing and sending Log and Event information from Unix/Linux and Windows systems (which produces Event Logs) and Devices (Routers, Firewalls, Switches, Servers, etc) over UDP Port 514 to a centralized Log/Event Message collector which is known as a Syslog Server.
Must Read
How does syslog work Linux?
The syslog service, which receives and processes syslog messages. It listens for events by creating a socket located at /dev/log , which applications can write to. It can write messages to a local file or forward messages to a remote server. There are different syslog implementations including rsyslogd and syslog-ng.
Marcus Vance is a cybersecurity auditor and technology writer dedicated to educating the public about online safety, data privacy regulations, enterprise security, and emerging cyber threats.
